Installing and configuring an RMT server
RMT (Repository Mirroring Tool) is a proxy system that mirrors software repositories and registers client machines within a private network. By acting as a local intermediary for SUSE Customer Center, RMT enables administrators to manage package updates and client registrations locally without direct external Internet access for every system, significantly enhancing network security and reducing bandwidth usage.
- REQUIREMENTS
A SUSE Linux Enterprise Server 16.1 system.
Valid SUSE Customer Center organization credentials.
Sufficient local storage space (approximately 1.5 times the size of all enabled repositories).
1 Introduction #
This article describes how to run an RMT server on SUSE Linux Enterprise Server 16.1. Install RMT directly during the installation of SUSE Linux Enterprise Server or install it on a running system. After the packages are installed, use Ansible to do an initial configuration.

Configuring a server to be an RMT server installs and configures the NGINX Web server, listening on port 80. However, configuring a machine to be an installation server automatically installs the Apache Web server and configures it to listen on port 80.
Do not try to enable both these functions on the same server. It is not possible for a single server to host both simultaneously.
2 RMT server storage and disk space requirements #
The amount of storage your RMT server requires depends on several variables: the number of repositories and architectures that you mirror, and the number of products that are enabled. As a general guide, 1.5 times the total size of all enabled repositories should be sufficient. This is about 200 GB per SUSE Linux Enterprise release, including all extensions.
Downloaded packages are stored in
/var/lib/rmt/public/repo/. Plan the size of the file
system that contains /var/lib/rmt accordingly.
The rmt-server package also installs the symbolic link
/usr/share/rmt/public/repo, which points to
/var/lib/rmt/public/repo/. Because the link is part
of the package and RMT writes only to
/var/lib/rmt, mirroring also works on systems where
/usr is read-only, such as immutable systems.

/tmp runs out of space
When RMT mirrors repositories from SUSE Customer Center, it writes large temporary files in /tmp.
If /tmp is too small, or is part of the /root file system, and
this file system is small in size, /tmp quickly runs out of space, resulting in a mirroring failure.
For more information, refer to https://support.scc.suse.com/s/kb/RMT-mirroring-fails-when-tmp-runs-out-of-disk-space?language=en_US.
3 Installing RMT during system installation #
Install RMT while installing SUSE Linux Enterprise Server with Agama by adding the rmt-server package to the installation profile.
RMT is not available as a software pattern, and the Agama Web
interface only lets you select patterns. To install RMT during
installation, add the rmt-server package to the
software section of an Agama installation profile:
"software": {
  "packages": [
    "rmt-server"
  ]
}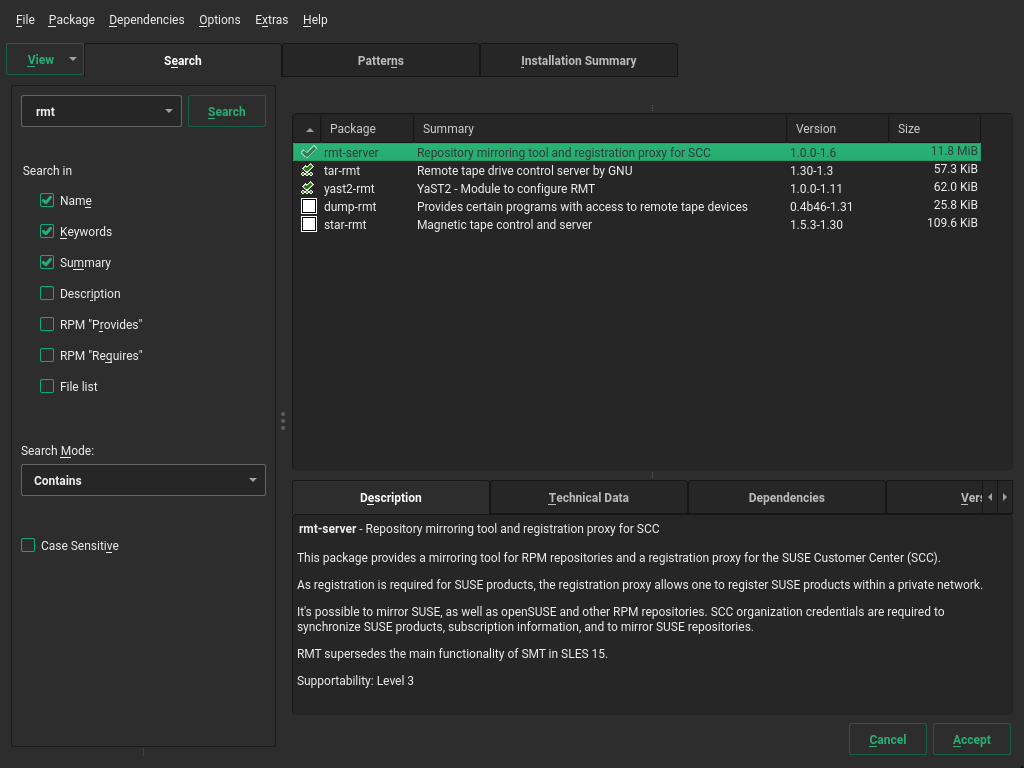
The rmt-server package is available from the SUSE Linux Enterprise Server product repository, so no additional repository is required. If you install with the Agama Web interface instead, install RMT after the installation as described in Section 4, “Installing RMT on an existing SLES ”.
You can use the same machine both as an installation server that provides the installation media and as the RMT server. When installing client systems, specify this machine as the registration server.
Check for available RMT updates immediately after installing SLES
using the zypper patch command because SUSE
continuously releases maintenance updates for RMT.
4 Installing RMT on an existing SLES #
Install RMT on a running SUSE Linux Enterprise Server system with
zypper.
To install RMT on a running SUSE Linux Enterprise Server installation, use the
zypper command:
>sudozypper in rmt-server
5 Upgrading an RMT server from SUSE Linux Enterprise 15 to SLES 16.1 #
Carrying an existing RMT server across the distribution upgrade from SUSE Linux Enterprise 15 SP7 to SUSE Linux Enterprise Server 16.1 requires repairing two platform changes that leave RMT unavailable afterwards.
These two platform changes are:
Network stack replacement: SLES 16.1 completely removes the legacy
wickednetworking framework and standardizes on NetworkManager as the sole network control stack.Mandatory Access Control Framework: SLES 16.1 replaces
AppArmorwith SELinux toenforcingmode by default.
Upgrade the host itself using the distribution migration system, as described in Upgrading to SUSE Linux Enterprise Server 16.1. This section covers only the steps specific to a host running RMT.

The distribution migration system reports success for the distribution
upgrade, not for the services running on the host. Even when every
suse-migration-* unit finishes with
Result=success and
/var/log/distro_migration.exitcode contains
0, RMT does not start until you complete the steps
below.
5.1 Before the upgrade #
Back up the RMT configuration file and the RMT database to a location outside the host:
#cp /etc/rmt.conf /root/rmt.conf.backup#mysqldump --single-transaction rmt > /root/rmt.sqlRecord the ownership of the MariaDB data directory. On SUSE Linux Enterprise 15, as it belongs to the group
root, which breaks MariaDB after the upgrade:#ls -ld /var/lib/mysqldrwx------ 1 mysql root 442 /var/lib/mysql
The upgrade replaces wicked
with NetworkManager, which changes the DHCP client identifier. Consequently, a host using DHCP
is likely to receive a new IP address. Because clients registered
against this RMT server reach it through the URL stored in their
Zypper service definitions, assign the server a stable IP address or
host name before upgrading.
5.2 After the upgrade #
Check which services are running. RMT depends on MariaDB through
Requires=mariadb.service, so a failed database keeps RMT inactive:#systemctl --failed#systemctl is-active mariadb nginx rmt-serverCorrect the group ownership of the MariaDB data directory:
#chgrp -R mysql /var/lib/mysqlOn SUSE Linux Enterprise Server 16.1,
mariadb.servicecombinesStateDirectory=mysqlwithUser=mysqlandGroup=mysql. systemd therefore adjusts the ownership of/var/lib/mysqlon every start, and themysql:rootownership inherited from SUSE Linux Enterprise 15 makes that fail:mariadb.service: Failed to set up special execution directory in /var/lib: Permission denied mariadb.service: Control process exited, code=exited, status=238/STATE_DIRECTORY
The error is reported as a permission problem rather than an ownership one, which makes it easy to mistake for a file system or SELinux fault.
Start MariaDB:
#systemctl start mariadbAllow nginx to connect to the RMT back-end:
#setsebool -P httpd_can_network_connect onSUSE Linux Enterprise Server 16.1 uses SELinux in enforcing mode instead of AppArmor. The
httpd_can_network_connectboolean is off by default, which prevents nginx from opening a connection to the RMT back-end on127.0.0.1:4224. Without this setting, nginx answers every request that it proxies to RMT with502.Verify that RMT answers correctly:
#curl -o /dev/null -w '%{http_code}\n' http://localhost/connect/subscriptions/products401#curl -o /dev/null -w '%{http_code}\n' http://localhost/repo/200401is the expected answer on the registration endpoint: it shows that the RMT application is reachable and requires authentication. A502means that the previous step is incomplete.Restart the host and repeat the checks. Confirming the changes across a reboot is essential: SELinux boolean only persists when it is set with
-P, and MariaDB may not be independently enabled sincermt-server.servicemanages it viaRequires=.
SUSE Linux Enterprise 15 SP7 offers both RMT 2 and RMT 3, while SUSE Linux Enterprise Server 16.1 ships only RMT 3. A host still running RMT 2 therefore moves to RMT 3 as part of the distribution upgrade.
No action is required. /etc/rmt.conf and the
contents of the database are preserved, and
rmt-server-migration.service updates the database
schema before rmt-server.service starts. RMT 3
differs from RMT 2 in the Ruby and Rails versions it runs on,
not in its configuration file or its
rmt-cli commands.
Confirm the version after the upgrade:
#rmt-cli version
nginx serves /repo/ directly from disk, so clients
continue to download packages even when the RMT application is
unreachable and no client can register. Check the registration
endpoint, not just the repository paths.
6 Deploying RMT on top of the Kubernetes cluster #
This section describes how to deploy RMT on a Kubernetes cluster. It uses Helm as the package manager to interact with the Kubernetes cluster. Find more details about using Helm at https://helm.sh/docs/intro/using_helm/.
6.1 Prerequisites #
Running Kubernetes cluster
helmcommand configured to interact with the clusterA storage class for the persistent volumes of RMT and MariaDB. The example in Section 6.3, “The
values.yamlfile” uses thelocal-pathstorage class, which is only available in Rancher workloads. On other clusters, install thelocal-pathstorage provisioner:>kubectl apply -f https://raw.githubusercontent.com/rancher/local-path-provisioner/v0.0.26/deploy/local-path-storage.yamlAlternatively, set
app.storage.classanddb.storage.classto a storage class that already exists in your cluster.
6.2 Application components #
Each component of the RMT application is deployed in its own container. RMT consists of the following components:
- RMT server
Containerized version of the RMT application server with the ability to pass its configuration via Helm values. Storage is done on a volume that is allocated to the Kubernetes cluster. You need to adjust the size of the storage depending on the number of repositories you need to mirror.
- MariaDB
The database back-end for RMT. No post-installation task is needed since RMT creates the required database and tables at start-up. If passwords are not specified in the
values.yamlfile, they are generated automatically.- nginx
A Web server configured for RMT routes. Having a properly configured Web server allows you to target your Ingress traffic (for RMT) to this nginx service directly. You do not need to configure Ingress for RMT -specific path handling, as nginx is configured to take care of this itself.
6.3 The values.yaml file #
The RMT chart includes the values.yaml file
where all parameters are documented and their default values are
defined. You can override these values by providing your own values
file, for example:
> cat << EOF > rmt-config.yaml
---
app:
  storage:
    class: local-path1
  scc:
    enabled: false
    username: "UXXXXXXX"
    password: "PASSXXXX"
    products_enable:
      - SLES/15.3/x86_64
      - sle-module-python2/15.3/x86_64
    products_disable:
      - sle-module-legacy/15.3/x86_64
      - sle-module-cap-tools/15.3/x86_64
db:
  storage:
    class: local-path2
ingress:
  enabled: true
  hosts:
    - host: chart-example.local
      paths:
        - path: "/"
          pathType: Prefix
  tls:
    - secretName: rmt-cert
      hosts:
        - chart-example.local
EOFThe storage class for the RMT and MariaDB persistent volumes. The storage class must exist in the cluster, see Section 6.1, “Prerequisites”. |
And to install RMT, run:
> helm install rmtsle oci://registry.suse.com/suse/rmt-helm -f rmt-config.yaml6.3.1 Required values #
- Key: app.scc.password
Type: string
Default:
nilDescription: SUSE Customer Center proxy password. The password string needs to be put inside quotes. If the quote character
"is part of the string, it has to be escaped with\.- Key: app.scc.username
Type: string
Default:
nilDescription: SUSE Customer Center proxy user name. The user name string needs to be put inside quotes. If the quote character
"is part of the string, it has to be escaped with\.- Key: app.scc.products_enable
Type: list
Default:
[]Description: list of products to enable for mirroring
- Key: app.scc.products_disable
Type: list
Default:
[]Description: list of products to disable for mirroring
- Key: app.storage.class
Type: string
Default:
""Description: Kubernetes
storageclass.- Key: db.storage.class
Type: string
Default:
""Description: Kubernetes
storageclass.- Key: ingress.enabled
Type: bool
Default:
falseDescription: Ingress Enabled
- Key: ingress.hosts[0]
Type: object
Default:
{"host":"chart-example.local","paths":[{"path":"/","pathType":"Prefix"}]}Description: DNS name at which the RMT service will be accessible from clients
- Key: ingress.tls[0].hosts[0]
Type: string
Default:
"chart-example.local"Description: DNS name at which the RMT service will be accessible from clients
- Key: ingress.tls[0].secretName
Type: string
Default:
"rmt-cert"Description: TLS Ingress Certificate
7 Configuring RMT with Ansible #
Configure RMT with Ansible as described in the following procedure. The ansible-rmt-server package provides pre-built playbooks and roles for automated RMT configuration.
Navigate to the Ansible configuration directory:
#cd /usr/share/ansible/rmtCreate the configuration file
group_vars/all.ymlbased on the provided example:#cp group_vars/all.yml.example group_vars/all.ymlEdit
group_vars/all.ymland configure the following variables:rmt_db_usernameDatabase user name for RMT (default:
rmt)rmt_db_passwordSecure password for the RMT database user
RMT_ORGANIZATION_USERNAMEYour SUSE Customer Center organization credentials. To retrieve your credentials, refer to Mirroring credentials.
RMT_ORGANIZATION_PASSWORDYour SUSE Customer Center organization password
Example configuration:
---
rmt_db_username: rmt
rmt_db_password: "your_secure_password"

rmt:
  RMT_ORGANIZATION_USERNAME: "your_scc_username"
  RMT_ORGANIZATION_PASSWORD: "your_scc_password"
Run the Ansible playbook to configure RMT:
#ansible-playbook site.ymlThe playbook will automatically perform the following tasks:
Install required dependencies (MariaDB, nginx, Python modules)
Configure and start the MariaDB database service
Create the RMT database and database user
Generate SSL certificates for HTTPS
Configure nginx virtual hosts
Create
/etc/rmt.confconfiguration fileRun database migrations
Start and enable the RMT server service
On systems with SELinux in enforcing mode, allow nginx to connect to the RMT back end service:
#setsebool -P httpd_can_network_connect 1Verify the installation by checking the API health status:
#curl -s http://localhost/api/health/status{"state":"online"}

The Ansible playbook generates SSL certificates at the following locations:
- CA certificate
/etc/rmt/ssl/rmt-ca.crt- CA private key
/etc/rmt/ssl/rmt-ca.key- Server certificate
/etc/rmt/ssl/rmt-server.crt- Server private key
/etc/rmt/ssl/rmt-server.key
8 Enabling SLP announcements #
Enable SLP (Service Location Protocol) announcements so that clients can discover the RMT service on the network.
RMT includes the SLP service description file
/etc/slp.reg.d/rmt-server.reg. To enable SLP
announcements of the RMT service, follow these steps:
If
firewalldis running:Open relevant ports:
>sudofirewall-cmd --permanent --add-port=427/tcp success>sudofirewall-cmd --permanent --add-port=427/udp successReload the
firewalldconfiguration:>sudofirewall-cmd --reload
Verify that the SLP server is installed and install it if it is not:
>sudozypper install openslp-serverEnable and start the SLP service:
>sudosystemctl enable --now slpd.service
9 Accessing SUSE Customer Center from behind a firewall #
Allow the RMT server to reach SUSE Customer Center when it is located behind a
firewall that does not support host name allowlisting.
If the RMT server is behind a firewall and cannot access SUSE Customer Center directly, you need to allow connections to the following domains on both 80 and 443 ports on the firewall.
scc.suse.com
updates.suse.com
installer-updates.suse.com
If the firewall you are using does not support allowing connections from
host names —such as firewalld— allow connections to the below corresponding IP addresses.
Resolve the IP address of the domain, for example,
installer-updates.suse.com.>nslookup installer-updates.suse.com[...] Address: 152.199.22.115Add firewall rules for ports 80 and 443 for each discovered IP address.
Port 80:
>sudofirewall-cmd --permanent --zone=public \ --add-rich-rule='rule family="ipv4" source address="152.199.22.115" \ port protocol="tcp" port="80" accept'Port 443:
>sudofirewall-cmd --permanent --zone=public \ --add-rich-rule='rule family="ipv4" source address="152.199.22.115" \ port protocol="tcp" port="443" accept'
Reload the firewall configuration.
>sudofirewall-cmd --reload
10 RMT configuration files #
Reference of the options in the main RMT configuration file
/etc/rmt.conf and of the SSL certificate
locations used by RMT.
The main RMT configuration file is /etc/rmt.conf.
Configuration is performed using the Ansible playbooks provided in the
ansible-rmt-server package.
10.1 Main configuration file /etc/rmt.conf #
The initial configuration is performed using Ansible. Only the proxy configuration needs to be entered manually. The other configuration parameters are documented for reference.
All available configuration options can be found in the
/etc/rmt.conf file.
10.1.1 Mirroring settings #
The mirroring section lets you adjust mirroring
behavior.
mirror_srcDecides whether to mirror source RPM packages (architecture is
src).dedup_methodCreates hard links during mirroring when set to
hardlink. If the file system does not support hard links, it can be set tocopyinstead. Possible values:hardlink,copy.
10.1.2 HTTP client settings #
The http_client section defines the global HTTP
connection settings of RMT.
verboseEnables additional debug output to the
systemdjournal.proxyThe proxy server URL including the protocol and the port number. For example:
http://proxy_url:8080.noproxyA list of domains that should not go through the proxy, separated by commas. For example:
localhost.mylocaldomain.proxy_authThis setting determines the proxy authentication mechanism. Possible values are:
none,basic,digest,gssnegotiate,ntlm,digest_ie,ntlm_wb.proxy_userThe proxy server user name.
proxy_passwordThe proxy server password.
low_speed_limitLower speed limit when a download should be aborted in bytes/sec.
low_speed_timeTime until a download gets aborted, when download speed is below
low_speed_limit.
10.1.3 Settings for accessing SUSE repositories #
The scc section contains your mirroring
credentials for contacting SUSE Customer Center. To obtain your mirroring
credentials, see
Mirroring credentials.
Valid configuration keys for the section are:
usernameMirroring credentials user name.
passwordMirroring credentials password.
10.1.4 Web server settings #
The web_server section lets you tune the performance of your RMT server.
min_threadsSpecifies the minimum number of threads that an RMT server worker should spawn.
Acceptable values: Integer greater than or equal to 1.
max_threadsSpecifies the maximum number of threads that an RMT server worker should spawn.
Acceptable values: Integer greater than or equal to 1.
workersSpecifies the number of Web workers for RMT.
Acceptable values: Integer greater than or equal to 1.
11 Managing TLS/SSL certificates #
Regenerate the TLS/SSL certificates of your RMT server using the Ansible playbook when they expire.
11.1 SSL certificates and HTTPS #
By default access to API endpoints consumed by
SUSEConnect is limited to HTTPS only. nginx is
configured to use an SSL certificate and a private key from the following
locations:
Certificate:
/etc/rmt/ssl/rmt-server.crtPrivate key:
/etc/rmt/ssl/rmt-server.key
The Ansible playbook generates a custom certificate authority which is used to sign HTTPS certificates. This means that to register, this certificate authority must be trusted by the client machines:
For registrations during installation from the media or with YaST Registration module, a message will appear, prompting to trust the server certificate.
For registering a client system on the command line, use the
rmt-client-setupscript.
11.2 Regenerating HTTPS certificates #
HTTPS certificates should be regenerated before they expire. No additional actions are required on the client machines registered to the RMT server if only HTTPS certificates are regenerated.
The playbook generates a self-signed server certificate that carries
neither a common name nor subject alternative names, and that is not
signed by the CA certificate in
/etc/rmt/ssl/rmt-ca.crt. Clients that verify host
names reject such a certificate. If your clients verify the server
certificate, issue one yourself with a common name, the required
subject alternative names and a signature from your CA, then store it
as /etc/rmt/ssl/rmt-server.crt together with its
key in /etc/rmt/ssl/rmt-server.key. Note that any
subsequent run of the playbook overwrites both files.
Stop nginx and rmt-server services.
#systemctl stop nginx#systemctl stop rmt-serverRemove previously generated certificates.
#rm /etc/rmt/ssl/rmt-server.*Regenerate certificates using the Ansible playbook:
#cd /usr/share/ansible/rmt#ansible-playbook site.yml
11.3 Regenerating CA certificates and HTTPS certificates #
CA certificates can be regenerated after they have expired or in case of security issues.
The newly generated CA certificate must be imported on all clients
registered to the RMT server. This can be done by running the
rmt-client-setup script on the client machines.
Stop nginx service. rmt-server services.
#systemctl stop nginxStop rmt-server service.
#systemctl stop rmt-serverRemove previously generated CA and HTTPS certificates.
#rm /etc/rmt/ssl/rmt-ca.* rm /etc/rmt/ssl/rmt-server.*Regenerate certificates using the Ansible playbook:
#cd /usr/share/ansible/rmt#ansible-playbook site.yml
12 For more information #
To learn more about RMT, refer to the following resource:
13 Legal Notice #
Copyright© 2006– 2026 SUSE LLC and contributors. All rights reserved.
Permission is granted to copy, distribute and/or modify this document under the terms of the GNU Free Documentation License, Version 1.2 or (at your option) version 1.3; with the Invariant Section being this copyright notice and license. A copy of the license version 1.2 is included in the section entitled “GNU Free Documentation License”.
For SUSE trademarks, see https://www.suse.com/company/legal/. All other third-party trademarks are the property of their respective owners. Trademark symbols (®, ™ etc.) denote trademarks of SUSE and its affiliates. Asterisks (*) denote third-party trademarks.
All information found in this book has been compiled with utmost attention to detail. However, this does not guarantee complete accuracy. Neither SUSE LLC, its affiliates, the authors, nor the translators shall be held liable for possible errors or the consequences thereof.
GNU Free Documentation License
Copyright (C) 2000, 2001, 2002 Free Software Foundation, Inc. 51 Franklin St, Fifth Floor, Boston, MA 02110-1301 USA. Everyone is permitted to copy and distribute verbatim copies of this license document, but changing it is not allowed.
0. PREAMBLE #
The purpose of this License is to make a manual, textbook, or other functional and useful document "free" in the sense of freedom: to assure everyone the effective freedom to copy and redistribute it, with or without modifying it, either commercially or non-commercially. Secondarily, this License preserves for the author and publisher a way to get credit for their work, while not being considered responsible for modifications made by others.
This License is a kind of "copyleft", which means that derivative works of the document must themselves be free in the same sense. It complements the GNU General Public License, which is a copyleft license designed for free software.
We have designed this License to use it for manuals for free software, because free software needs free documentation: a free program should come with manuals providing the same freedoms that the software does. But this License is not limited to software manuals; it can be used for any textual work, regardless of subject matter or whether it is published as a printed book. We recommend this License principally for works whose purpose is instruction or reference.
1. APPLICABILITY AND DEFINITIONS #
This License applies to any manual or other work, in any medium, that contains a notice placed by the copyright holder saying it can be distributed under the terms of this License. Such a notice grants a world-wide, royalty-free license, unlimited in duration, to use that work under the conditions stated herein. The "Document", below, refers to any such manual or work. Any member of the public is a licensee, and is addressed as "you". You accept the license if you copy, modify or distribute the work in a way requiring permission under copyright law.
A "Modified Version" of the Document means any work containing the Document or a portion of it, either copied verbatim, or with modifications and/or translated into another language.
A "Secondary Section" is a named appendix or a front-matter section of the Document that deals exclusively with the relationship of the publishers or authors of the Document to the Document's overall subject (or to related matters) and contains nothing that could fall directly within that overall subject. (Thus, if the Document is in part a textbook of mathematics, a Secondary Section may not explain any mathematics.) The relationship could be a matter of historical connection with the subject or with related matters, or of legal, commercial, philosophical, ethical or political position regarding them.
The "Invariant Sections" are certain Secondary Sections whose titles are designated, as being those of Invariant Sections, in the notice that says that the Document is released under this License. If a section does not fit the above definition of Secondary then it is not allowed to be designated as Invariant. The Document may contain zero Invariant Sections. If the Document does not identify any Invariant Sections then there are none.
The "Cover Texts" are certain short passages of text that are listed, as Front-Cover Texts or Back-Cover Texts, in the notice that says that the Document is released under this License. A Front-Cover Text may be at most 5 words, and a Back-Cover Text may be at most 25 words.
A "Transparent" copy of the Document means a machine-readable copy, represented in a format whose specification is available to the general public, that is suitable for revising the document straightforwardly with generic text editors or (for images composed of pixels) generic paint programs or (for drawings) some widely available drawing editor, and that is suitable for input to text formatters or for automatic translation to a variety of formats suitable for input to text formatters. A copy made in an otherwise Transparent file format whose markup, or absence of markup, has been arranged to thwart or discourage subsequent modification by readers is not Transparent. An image format is not Transparent if used for any substantial amount of text. A copy that is not "Transparent" is called "Opaque".
Examples of suitable formats for Transparent copies include plain ASCII without markup, Texinfo input format, LaTeX input format, SGML or XML using a publicly available DTD, and standard-conforming simple HTML, PostScript or PDF designed for human modification. Examples of transparent image formats include PNG, XCF and JPG. Opaque formats include proprietary formats that can be read and edited only by proprietary word processors, SGML or XML for which the DTD and/or processing tools are not generally available, and the machine-generated HTML, PostScript or PDF produced by some word processors for output purposes only.
The "Title Page" means, for a printed book, the title page itself, plus such following pages as are needed to hold, legibly, the material this License requires to appear in the title page. For works in formats which do not have any title page as such, "Title Page" means the text near the most prominent appearance of the work's title, preceding the beginning of the body of the text.
A section "Entitled XYZ" means a named subunit of the Document whose title either is precisely XYZ or contains XYZ in parentheses following text that translates XYZ in another language. (Here XYZ stands for a specific section name mentioned below, such as "Acknowledgements", "Dedications", "Endorsements", or "History".) To "Preserve the Title" of such a section when you modify the Document means that it remains a section "Entitled XYZ" according to this definition.
The Document may include Warranty Disclaimers next to the notice which states that this License applies to the Document. These Warranty Disclaimers are considered to be included by reference in this License, but only as regards disclaiming warranties: any other implication that these Warranty Disclaimers may have is void and has no effect on the meaning of this License.
2. VERBATIM COPYING #
You may copy and distribute the Document in any medium, either commercially or non-commercially, provided that this License, the copyright notices, and the license notice saying this License applies to the Document are reproduced in all copies, and that you add no other conditions whatsoever to those of this License. You may not use technical measures to obstruct or control the reading or further copying of the copies you make or distribute. However, you may accept compensation in exchange for copies. If you distribute a large enough number of copies you must also follow the conditions in section 3.
You may also lend copies, under the same conditions stated above, and you may publicly display copies.
3. COPYING IN QUANTITY #
If you publish printed copies (or copies in media that commonly have printed covers) of the Document, numbering more than 100, and the Document's license notice requires Cover Texts, you must enclose the copies in covers that carry, clearly and legibly, all these Cover Texts: Front-Cover Texts on the front cover, and Back-Cover Texts on the back cover. Both covers must also clearly and legibly identify you as the publisher of these copies. The front cover must present the full title with all words of the title equally prominent and visible. You may add other material on the covers in addition. Copying with changes limited to the covers, as long as they preserve the title of the Document and satisfy these conditions, can be treated as verbatim copying in other respects.
If the required texts for either cover are too voluminous to fit legibly, you should put the first ones listed (as many as fit reasonably) on the actual cover, and continue the rest onto adjacent pages.
If you publish or distribute Opaque copies of the Document numbering more than 100, you must either include a machine-readable Transparent copy along with each Opaque copy, or state in or with each Opaque copy a computer-network location from which the general network-using public has access to download using public-standard network protocols a complete Transparent copy of the Document, free of added material. If you use the latter option, you must take reasonably prudent steps, when you begin distribution of Opaque copies in quantity, to ensure that this Transparent copy will remain thus accessible at the stated location until at least one year after the last time you distribute an Opaque copy (directly or through your agents or retailers) of that edition to the public.
It is requested, but not required, that you contact the authors of the Document well before redistributing any large number of copies, to give them a chance to provide you with an updated version of the Document.
4. MODIFICATIONS #
You may copy and distribute a Modified Version of the Document under the conditions of sections 2 and 3 above, provided that you release the Modified Version under precisely this License, with the Modified Version filling the role of the Document, thus licensing distribution and modification of the Modified Version to whoever possesses a copy of it. In addition, you must do these things in the Modified Version:
Use in the Title Page (and on the covers, if any) a title distinct from that of the Document, and from those of previous versions (which should, if there were any, be listed in the History section of the Document). You may use the same title as a previous version if the original publisher of that version gives permission.
List on the Title Page, as authors, one or more persons or entities responsible for authorship of the modifications in the Modified Version, together with at least five of the principal authors of the Document (all of its principal authors, if it has fewer than five), unless they release you from this requirement.
State on the Title page the name of the publisher of the Modified Version, as the publisher.
Preserve all the copyright notices of the Document.
Add an appropriate copyright notice for your modifications adjacent to the other copyright notices.
Include, immediately after the copyright notices, a license notice giving the public permission to use the Modified Version under the terms of this License, in the form shown in the Addendum below.
Preserve in that license notice the full lists of Invariant Sections and required Cover Texts given in the Document's license notice.
Include an unaltered copy of this License.
Preserve the section Entitled "History", Preserve its Title, and add to it an item stating at least the title, year, new authors, and publisher of the Modified Version as given on the Title Page. If there is no section Entitled "History" in the Document, create one stating the title, year, authors, and publisher of the Document as given on its Title Page, then add an item describing the Modified Version as stated in the previous sentence.
Preserve the network location, if any, given in the Document for public access to a Transparent copy of the Document, and likewise the network locations given in the Document for previous versions it was based on. These may be placed in the "History" section. You may omit a network location for a work that was published at least four years before the Document itself, or if the original publisher of the version it refers to gives permission.
For any section Entitled "Acknowledgements" or "Dedications", Preserve the Title of the section, and preserve in the section all the substance and tone of each of the contributor acknowledgements and/or dedications given therein.
Preserve all the Invariant Sections of the Document, unaltered in their text and in their titles. Section numbers or the equivalent are not considered part of the section titles.
Delete any section Entitled "Endorsements". Such a section may not be included in the Modified Version.
Do not retitle any existing section to be Entitled "Endorsements" or to conflict in title with any Invariant Section.
Preserve any Warranty Disclaimers.
If the Modified Version includes new front-matter sections or appendices that qualify as Secondary Sections and contain no material copied from the Document, you may at your option designate some or all of these sections as invariant. To do this, add their titles to the list of Invariant Sections in the Modified Version's license notice. These titles must be distinct from any other section titles.
You may add a section Entitled "Endorsements", provided it contains nothing but endorsements of your Modified Version by various parties--for example, statements of peer review or that the text has been approved by an organization as the authoritative definition of a standard.
You may add a passage of up to five words as a Front-Cover Text, and a passage of up to 25 words as a Back-Cover Text, to the end of the list of Cover Texts in the Modified Version. Only one passage of Front-Cover Text and one of Back-Cover Text may be added by (or through arrangements made by) any one entity. If the Document already includes a cover text for the same cover, previously added by you or by arrangement made by the same entity you are acting on behalf of, you may not add another; but you may replace the old one, on explicit permission from the previous publisher that added the old one.
The author(s) and publisher(s) of the Document do not by this License give permission to use their names for publicity for or to assert or imply endorsement of any Modified Version.
5. COMBINING DOCUMENTS #
You may combine the Document with other documents released under this License, under the terms defined in section 4 above for modified versions, provided that you include in the combination all of the Invariant Sections of all of the original documents, unmodified, and list them all as Invariant Sections of your combined work in its license notice, and that you preserve all their Warranty Disclaimers.
The combined work need only contain one copy of this License, and multiple identical Invariant Sections may be replaced with a single copy. If there are multiple Invariant Sections with the same name but different contents, make the title of each such section unique by adding at the end of it, in parentheses, the name of the original author or publisher of that section if known, or else a unique number. Make the same adjustment to the section titles in the list of Invariant Sections in the license notice of the combined work.
In the combination, you must combine any sections Entitled "History" in the various original documents, forming one section Entitled "History"; likewise combine any sections Entitled "Acknowledgements", and any sections Entitled "Dedications". You must delete all sections Entitled "Endorsements".
6. COLLECTIONS OF DOCUMENTS #
You may make a collection consisting of the Document and other documents released under this License, and replace the individual copies of this License in the various documents with a single copy that is included in the collection, provided that you follow the rules of this License for verbatim copying of each of the documents in all other respects.
You may extract a single document from such a collection, and distribute it individually under this License, provided you insert a copy of this License into the extracted document, and follow this License in all other respects regarding verbatim copying of that document.
7. AGGREGATION WITH INDEPENDENT WORKS #
A compilation of the Document or its derivatives with other separate and independent documents or works, in or on a volume of a storage or distribution medium, is called an "aggregate" if the copyright resulting from the compilation is not used to limit the legal rights of the compilation's users beyond what the individual works permit. When the Document is included in an aggregate, this License does not apply to the other works in the aggregate which are not themselves derivative works of the Document.
If the Cover Text requirement of section 3 is applicable to these copies of the Document, then if the Document is less than one half of the entire aggregate, the Document's Cover Texts may be placed on covers that bracket the Document within the aggregate, or the electronic equivalent of covers if the Document is in electronic form. Otherwise they must appear on printed covers that bracket the whole aggregate.
8. TRANSLATION #
Translation is considered a kind of modification, so you may distribute translations of the Document under the terms of section 4. Replacing Invariant Sections with translations requires special permission from their copyright holders, but you may include translations of some or all Invariant Sections in addition to the original versions of these Invariant Sections. You may include a translation of this License, and all the license notices in the Document, and any Warranty Disclaimers, provided that you also include the original English version of this License and the original versions of those notices and disclaimers. In case of a disagreement between the translation and the original version of this License or a notice or disclaimer, the original version will prevail.
If a section in the Document is Entitled "Acknowledgements", "Dedications", or "History", the requirement (section 4) to Preserve its Title (section 1) will typically require changing the actual title.
9. TERMINATION #
You may not copy, modify, sublicense, or distribute the Document except as expressly provided for under this License. Any other attempt to copy, modify, sublicense or distribute the Document is void, and will automatically terminate your rights under this License. However, parties who have received copies, or rights, from you under this License will not have their licenses terminated so long as such parties remain in full compliance.
10. FUTURE REVISIONS OF THIS LICENSE #
The Free Software Foundation may publish new, revised versions of the GNU Free Documentation License from time to time. Such new versions will be similar in spirit to the present version, but may differ in detail to address new problems or concerns. See https://www.gnu.org/copyleft/.
Each version of the License is given a distinguishing version number. If the Document specifies that a particular numbered version of this License "or any later version" applies to it, you have the option of following the terms and conditions either of that specified version or of any later version that has been published (not as a draft) by the Free Software Foundation. If the Document does not specify a version number of this License, you may choose any version ever published (not as a draft) by the Free Software Foundation.
ADDENDUM: How to use this License for your documents #
Copyright (c) YEAR YOUR NAME.
Permission is granted to copy, distribute and/or modify this document
under the terms of the GNU Free Documentation License, Version 1.2
or any later version published by the Free Software Foundation;
with no Invariant Sections, no Front-Cover Texts, and no Back-Cover Texts.
A copy of the license is included in the section entitled “GNU
Free Documentation License”.
If you have Invariant Sections, Front-Cover Texts and Back-Cover Texts, replace the “with...Texts.” line with this:
with the Invariant Sections being LIST THEIR TITLES, with the
Front-Cover Texts being LIST, and with the Back-Cover Texts being LIST.
If you have Invariant Sections without Cover Texts, or some other combination of the three, merge those two alternatives to suit the situation.
If your document contains nontrivial examples of program code, we recommend releasing these examples in parallel under your choice of free software license, such as the GNU General Public License, to permit their use in free software.